Without secure boot and signed updates, a single compromised device or update server can take over a fleet. The CRA makes these controls a market requirement in the EU.
Unsigned software runs
Without secure boot, anyone with access can run their own code.
Weak key management
Keys on developer laptops put the whole fleet at risk.
CRA requirements
EU market access now depends on security by design and update obligations.
What we do
Secure boot implementation, key management process and security documentation.
Secure boot chain on your SoC
Key management and signing infrastructure
Encrypted storage and secrets handling
Hardening and attack surface reduction
CRA gap assessment and SBOM
How we work
Our Engineering Process
Keep deployed devices secure, updated and visible for their whole life.
1. Assessment
Your current update, security and monitoring setup reviewed.
2. Architecture
OTA, device identity, telemetry and remote access designed together.
3. Implementation
On-device agent, backend and dashboards built and integrated.
4. Staged rollout
Tested on a pilot group before it reaches the whole fleet.
5. Ongoing operations
Monitoring, releases and security updates over the product’s life.
How we added a verified boot chain, encrypted storage and a secure flashing tool to a European OEM’s Linux EV chargers, including units already installed, without changing the hardware.
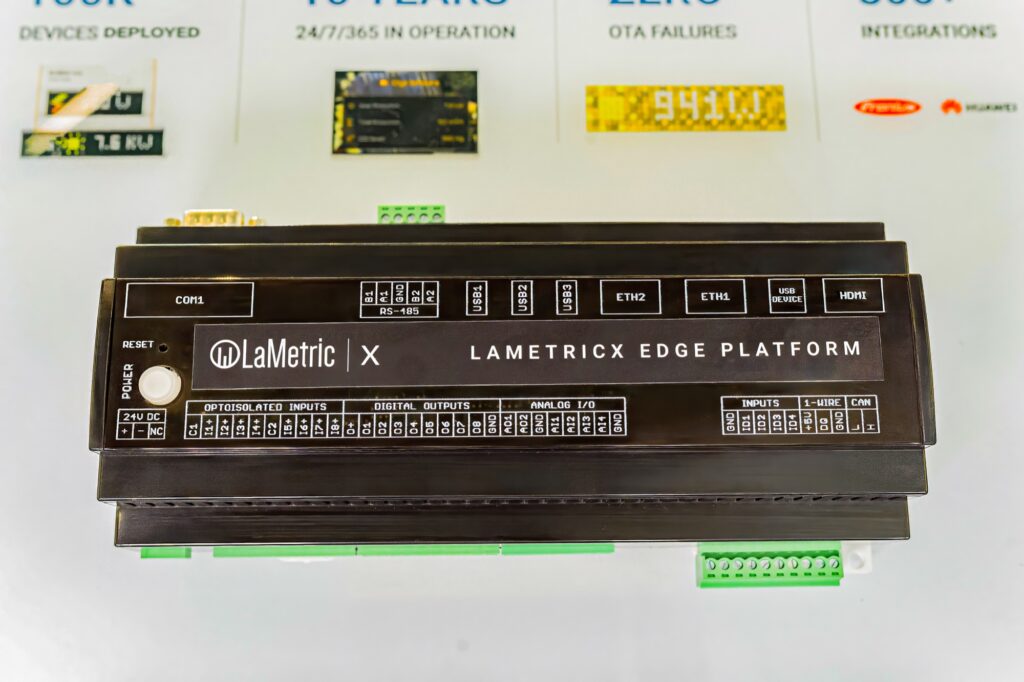
An edge energy management foundation built on the inverter, meter and battery integrations proven in our own LaMetric smart energy displays: Modbus and SunSpec, fully on site, steering EV chargers, heat pumps and water heating to solar surplus and cheaper tariffs.
Give every device a unique, trusted identity from the factory to the cloud: keys, certificates and a PKI that handles provisioning, rotation and revocation across the whole fleet.